Our pentest approach. Why most risk management teams are NOT future ready
5 May 2025 · 2 min read · Mr Strategy
You have a penetration testing process.
You have a risk management department.
You have an internal audit team.
Yet you are still vulnerable. Why?
Because most teams are not evolving as fast as the threat landscape.
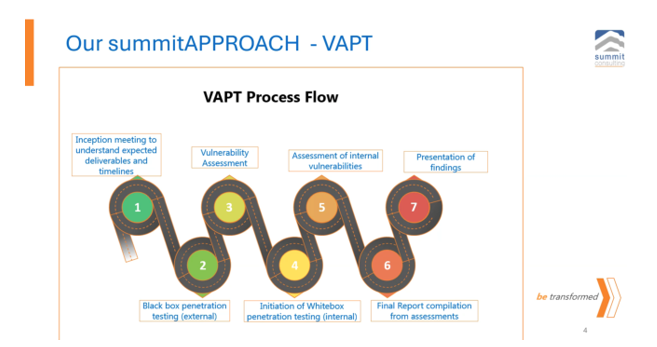
At Summit Consulting, our VAPT approach is simple and brutal:
- Inception meeting: Define timelines, expectations, and failure points up front.
- Blackbox penetration testing: Simulate a real-world external attack without insider knowledge.
- Vulnerability assessment: Identify cracks before the enemy does.
- Whitebox penetration testing: Simulate insider threats with full access.
- Internal vulnerabilities assessment: Your weakest links are always inside.
- Final report compilation: No sugar-coating. Just the truth.
- Presentation of findings: Executive-level intelligence, not geek talk.
- Inception meeting: Their IT head assured us, "We’re clean. Just do a quick scan."
- Blackbox testing: Within 4 hours, we breached their email gateway and sat silently inside their network.
- Vulnerability assessment: Found 47 high-risk exposures, including default admin credentials on core switches.
- Whitebox testing: Gained domain admin privileges in less than a day, with full access to their backup systems.
- Internal vulnerability check: Discovered weak passwords like "Welcome@123" and unpatched ERP servers.
- Final report: We drafted a 54-page red alert report with proof-of-exploit screenshots.
- Board presentation: Their CEO nearly fell out of his chair. His exact words were: "But our IT team said we were safe?"
Comments
No comments yet. Be the first to share your thoughts.