From passwords to passkeys-the future of digital identity
11 June 2025 · 4 min read · Mr Strategy
It all starts with a compromise
It always begins with a password.
In June 2024, a procurement officer at a large local firm used the same password, Brenda@2020, across her Gmail, Zoom, and company ERP. She thought no one would care. But someone did.
A hacker running a darknet scraping tool picked it up from a 2021 data breach dump. Within hours, they were in. Not just into her Gmail. But into internal payment systems. The hacker didn’t break down a door. He walked in with a borrowed key.
This is not just about weak passwords. It’s about passwords themselves. They’ve become the single point of failure in our digital lives.
The password paradox
Passwords were invented in the 1960s. But in 2025, they’re still guarding trillion-shilling systems, despite being laughably outdated.
Here’s the paradox:
The stronger your password, the harder it is to remember.
The easier it is to remember, the easier it is to hack.
This gives rise to the three horsemen of digital doom: Re-use. Predictability. Social engineering.
You can have the best firewall, but if your HR manager is using Godisgood@123, you're a ticking time bomb.
The phasing out of passwords: Enter passkeys
The future is passwordless.
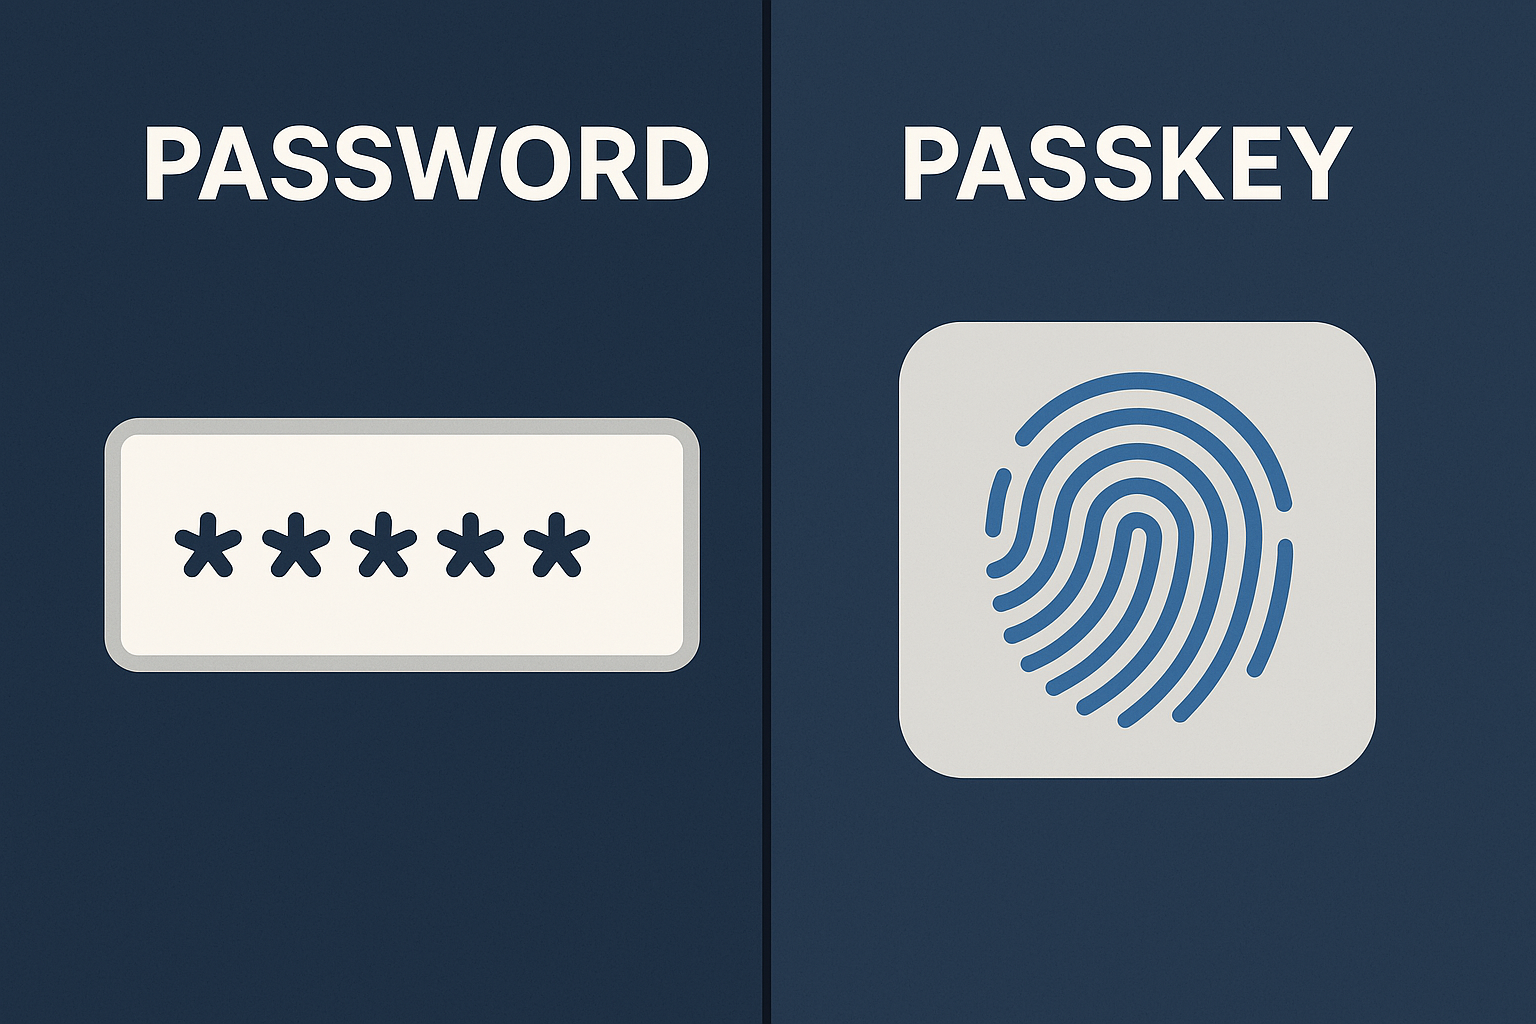
Tech giants like Google, Apple, and Microsoft have adopted passkeys, cryptographic credentials that never leave your device. Instead of typing a password, you use your fingerprint, face, or device PIN. The secret never travels across the internet. So it can’t be phished, stolen, or brute-forced.
Think of passkeys as digital locks with no keys. Only your face or finger can open them.
But here’s the real power: zero knowledge architecture. The server doesn’t even store your credentials. No more vaults to break into. No more passwords to leak.
What makes passkeys better
- a) They’re phishing-proof
- b) They’re seamless
- c) They’re device-bound
Comments
No comments yet. Be the first to share your thoughts.